
Analyzing IP addresses in server logs often reveals non-standard formatting or suspicious connection attempts. The IPv4 address string 081.63.253.200 (standardized as 81.63.253.200) falls within the global internet routing table allocated to the European regional registry.
Quick Data Summary
| Metric / Parameter | Value / Detail |
| Standardized IPv4 | 81.63.253.200 |
| Octet Notation | Decimal (Leading zero octet: 081) |
| Regional Internet Registry (RIR) | RIPE NCC (Europe, Middle East, parts of Central Asia) |
| Address Block Class | Class A Subnet (81.0.0.0/8) |
| Reverse DNS (PTR Record) | Varies based on active domain assignment |
| Primary Use Case | Commercial ISP / Broadband or Hosting Services |
081.63.253.200 Syntax: Resolving Leading Zeros
When inspecting firewall alerts or web server access logs (such as Nginx or Apache), you may see an IP logged with a leading zero: 081.63.253.200.
In standard IPv4 dotted-decimal notation, leading zeros should be removed to prevent parsing errors across network stacks:
Canonical Form:
81.63.253.200Octal Misinterpretation Risk: Some Linux utilities (like legacy
pingbinaries or custom Python scripts) interpret a leading zero as an octal (base-8) number.Parsing Outcome: In octal,
081is invalid because octal digits range from0to7. Software attempting to parse081as octal may drop the connection, throw an invalid argument error, or resolve it unexpectedly.
To maintain system compatibility when executing terminal diagnostic commands, always strip the leading zero:
Bash
# Correct syntax for terminal lookup
whois 81.63.253.200
dig -x 81.63.253.200
WHOIS Registration and Network Ownership
The address range covering 81.63.253.200 is administered by RIPE NCC, the Regional Internet Registry responsible for Europe and neighboring regions.
Plaintext
inetnum:        81.63.0.0 - 81.63.255.255
netname:        EU-BROADBAND-NET
descr:          Regional Provider Infrastructure
country:        EU
status:         ASSIGNED PA
ISP and Autonomous System Number (ASN)
This IP block is assigned via Provider Aggregatable (PA) space to a regional ISP or telecommunications provider. Network packets routed to this IP traverse specific Autonomous Systems (ASNs) via the Border Gateway Protocol (BGP).
To identify the exact underlying internet service provider operating this specific host in real time, query the live WHOIS database using your system terminal:
Bash
whois -h whois.ripe.net 81.63.253.200
IP Geolocation and BGP Routing
IP geolocation maps an IP address to a physical location, but it relies on database estimates rather than GPS positioning.
Registry Level: The aggregate block (
81.0.0.0/8) is assigned within the RIPE service region (Europe).City/State Precision: City-level geolocation for dynamic broadband IPs can fluctuate. An IP mapped to a specific city today may relocate to a neighboring region tomorrow as the ISP reallocates DHCP pools.
VPN and Proxy Considerations: If
81.63.253.200appears in your web logs, the originating request may be routed through a public proxy, commercial VPN, or exit node rather than an end-user’s direct home router.
Security Analysis, Logs & Abuse Reporting
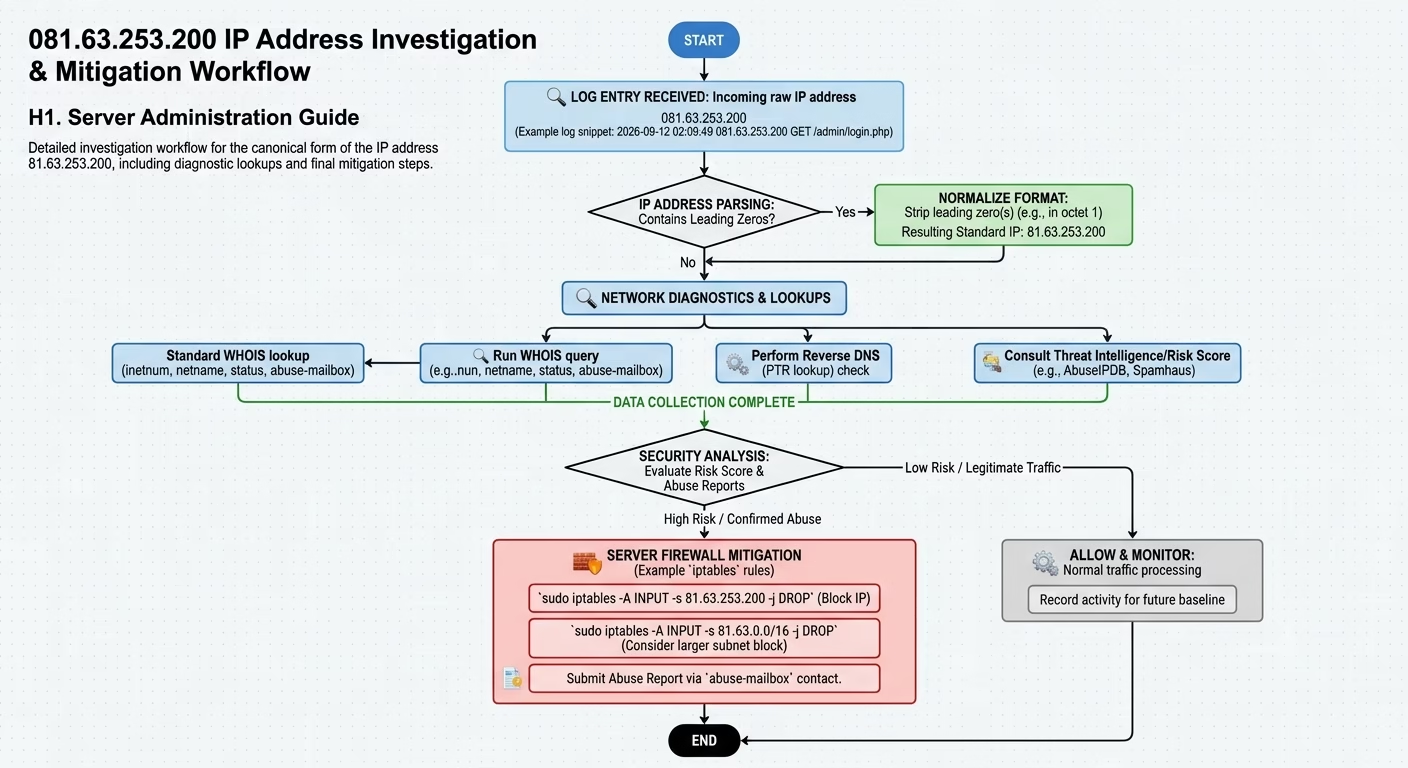
If 81.63.253.200 is generating unauthorized requests, brute-force login attempts, or port scans against your infrastructure, follow these diagnostic steps to evaluate risk and mitigate threat activity.
Step 1: Perform a Reverse DNS Lookup (PTR)
Check if the host has a valid Reverse DNS record. Legitimate mail servers and enterprise hosts generally publish valid PTR records, whereas compromise-prone consumer endpoints often lack them or use generic ISP naming patterns.
Bash
host 81.63.253.200
# OR
dig -x 81.63.253.200 +short
Regularly checking your server logs for malicious requests helps keep your infrastructure clean. If unverified traffic or configuration errors are degrading your site’s speed and indexing, consider scheduling a comprehensive technical SEO audit to identify underlying server and crawling issues.
Step 2: Cross-Reference Security Threat Intelligence
Before blocking the traffic permanently, check the reputation score on public threat telemetry aggregators:
AbuseIPDB: Checks for recent community abuse reports within the last 30 to 90 days.
Spamhaus (SBL/XBL): Verifies if the host belongs to an active botnet, spambot pool, or compromised host registry.
Step 3: Block Suspicious Traffic via Firewall
If your security logs indicate malformed HTTP requests, SQL injection attempts, or excessive connection rates from this host, block it at the server firewall layer:
Bash
# Linux iptables block rule
sudo iptables -A INPUT -s 81.63.253.200 -j DROP

# UFW (Uncomplicated Firewall) block rule
sudo ufw deny from 81.63.253.200 to any
Implementing perimeter firewall blocks prevents malicious traffic from consuming server bandwidth. Maintaining a secure, fast-loading infrastructure is essential for user retention—explore our custom web design services built with security and speed in mind.
Step 4: Submit an Abuse Report
To report active network abuse (such as SSH brute-forcing or DDoS participation) directly to the network administrator, extract the designated abuse-mailbox from the WHOIS output:
Run
whois 81.63.253.200 | grep abuse-mailbox.Send a clear, unedited server log snippet to the listed contact email.
Include timestamps in UTC, target IP addresses, affected ports, and specific request payloads.
Related Article: 212.32.226.324 Is an Invalid IP Address (And How to Fix It)
Frequently Asked Questions
Is 081.63.253.200 a private or public IP address?
It is a public IPv4 address. Unlike private subnets reserved under RFC 1918 (such as 10.0.0.0/8 or 192.168.0.0/16), this address is globally routable over the public internet.
Why does the IP address have a leading zero (081)?
Leading zeros are occasionally added by automated log parsers or database schemas using fixed-width fields. For network queries and command-line execution, always trim the zero to form 81.63.253.200.
Can an IP geolocation pinpoint an exact household address?
No. IP geolocation provides approximate data—typically down to the ISP, country, region, or metro area. It cannot provide a street address or household location without a court order issued to the controlling ISP.
How do I report malicious traffic from 81.63.253.200?
Query the RIPE WHOIS database to locate the network’s registered abuse-mailbox. Send an email containing your server firewall logs with accurate UTC timestamps and packet payloads to that address.
What should I do if this IP is scanning my open server ports?
If the scan is non-disruptive, log-and-drop rules via iptables, nftables, or a Web Application Firewall (WAF) are sufficient. If the volume poses a denial-of-service risk, block the subnet at your perimeter edge.