
If you encountered the string 164.68.1111.161 in a server log, application configuration, or web input field, your system likely rejected it with an “Invalid IP Address” or “Format Error.”
164.68.1111.161 is mathematically and architecturally impossible under standard Internet Protocol version 4 (IPv4) rules.
An IPv4 address consists of four numbers separated by periods, where each number must fall strictly between 0 and 255. The third segment in this string—1111—violates the fundamental rules of computer networking established in RFC 791 IPv4 specifications.
This guide breaks down why this error occurs, how to locate the real IP address behind the typo, how to enforce proper IP validation in your code, and how to convert valid IPv4 addresses between binary, decimal, and hexadecimal formats.
Why 164.68.1111.161 Is an Invalid IP Address
To understand why 164.68.1111.161 fails, we have to look at how computers process network addresses at the hardware and protocol levels.
The 8-Bit Limit: Why Octets Cannot Exceed 255
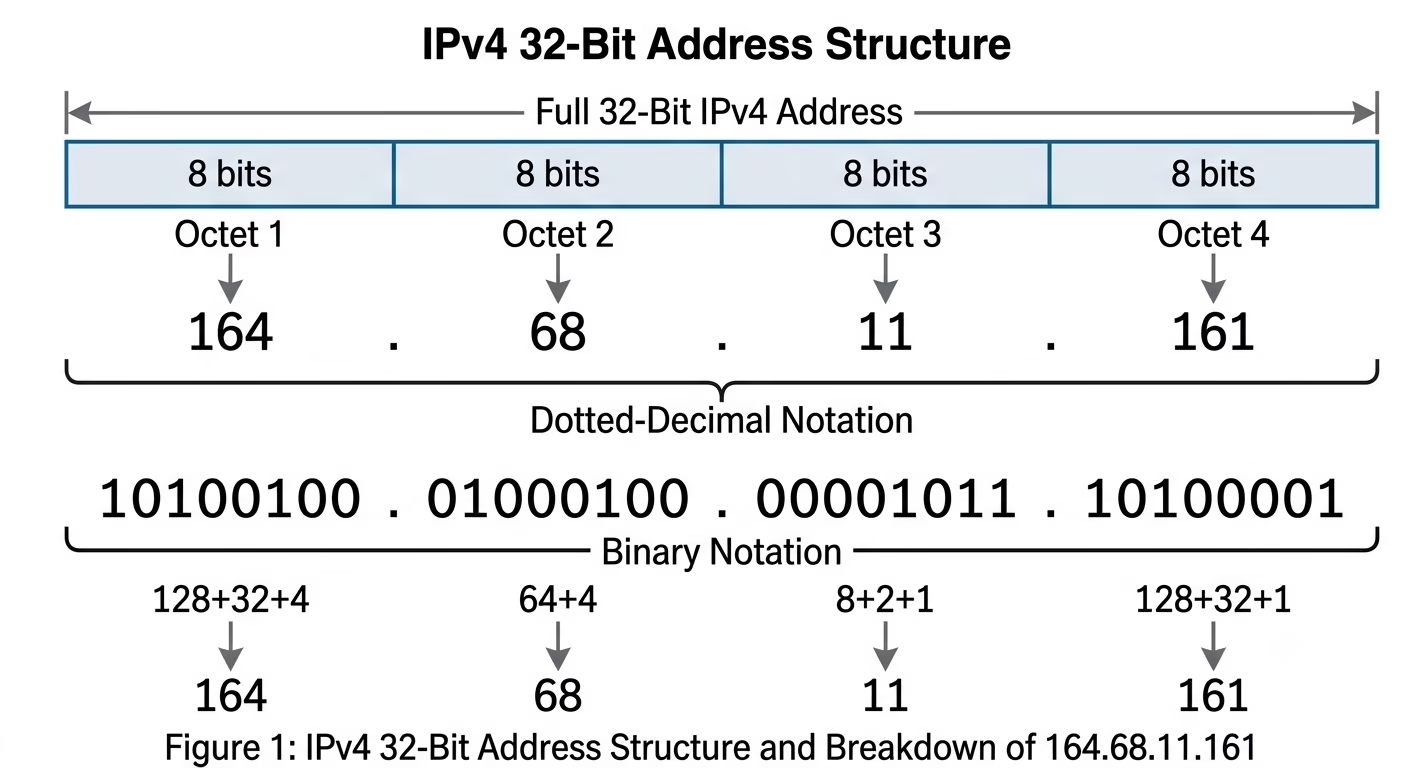
An IPv4 address is a 32-bit binary number. To make these numbers easier for humans to read, the 32 bits are divided into four 8-bit sections called octets, separated by dots (dotted-decimal notation).
32 Bits Total = [8 bits] . [8 bits] . [8 bits] . [8 bits]
Because an octet consists of exactly 8 binary digits (bits), the minimum and maximum values it can hold are calculated as follows:
Minimum value (all bits 0): $00000000_2 = 0_{10}$
Maximum value (all bits 1): $11111111_2 = 255_{10}$
Because $2^8 = 256$ total possible values (0 through 255), no single octet in an IPv4 address can ever be greater than 255.
Identifying the Typo in 164.68.1111.161
Analyzing 164.68.1111.161 octet by octet reveals the specific point of failure:
| Octet Position | Value in String | Status | Reason |
| First Octet | 164 | Valid | Between 0 and 255 |
| Second Octet | 68 | Valid | Between 0 and 255 |
| Third Octet | 1111 | Invalid | Exceeds maximum limit of 255 |
| Fourth Octet | 161 | Valid | Between 0 and 255 |
The value 1111 would require roughly 11 bits of storage space ($1111_{10} = 10001010111_2$), breaking the 32-bit IPv4 protocol layout.
Common Causes of the 1111 Typo
When analyzing malformed IP strings in production server logs, this specific format error usually traces back to one of three issues:
Keystroke Duplication: A user or administrator intended to type
11or111(if in a custom subnetwork context, though111is still valid), but key-repeat produced1111.Missing Octet Delimiter: Two distinct numbers were pushed together due to a dropped dot (e.g., intending to type
164.68.11.1161or164.68.1.111).Contaminated Log Parsing: A regex string split or log aggregation script improperly concatenated adjacent port numbers or database IDs into the IP string field.
If you are attempting to trace the ownership check the IANA IPv4 Address Space Registry to identify which Regional Internet Registry manages the 164.68.0.0/16 block. of 164.68.x.x, the /16 block 164.68.0.0/16 belongs to public IP space managed by regional Internet registries (RIRs). The valid target IP is likely 164.68.11.161 or 164.68.111.161.
How to Identify and Fix Common IPv4 Syntax Errors
When handling user inputs, configuration files, or API endpoints, several recurring structural errors cause IP validation failures.
Common IPv4 Formatting Mistakes:

[164.68.1111.161] ----> Octet Value Overflow (> 255)
[164.68.11.161.5] ----> Too Many Octets (5 instead of 4)
[164.68.11] -----------> Missing Octets (3 instead of 4)
[164.068.11.161] ------> Leading Zero (Interpreted as Octal)
1. Octet Value Overflow
The Problem: An octet contains a value higher than 255 (e.g.,
192.168.1.300).The Fix: Audit the input source. If working with subnetting, verify whether a subnet mask or broadcast address was accidentally pasted into a host IP field.
Similar to the 164.68.1111.161 error, other octet overflow typos—such as the 212.32.226.324 invalid IP error—occur when a single 8-bit segment exceeds the 255 maximum value limit.
2. Incorrect Octet Count
The Problem: The string has fewer or more than four segments (e.g.,
10.0.1or192.168.1.1.1).The Fix: Ensure the string follows the explicit
A.B.C.Dformat. In networking software, shortened representations like10.1can sometimes be parsed as10.0.0.1by socket libraries, but strict web validation tools will reject them.
3. Leading Zeros (Octal Interpretation Issues)
The Problem: Entering
192.168.010.1.The Fix: Some operating systems and programming languages (like C or old Python libraries) read numbers starting with
0as octal (base-8). In octal,010equals8in decimal. To prevent unexpected routing or validation failure, strip leading zeros from every octet before parsing.
Formatting errors can also happen when adding leading zeros to octets. For instance, an entry like 081.63.253.200 can fail validation or be incorrectly parsed as octal by legacy system libraries.
Validating IPv4 Addresses in Code and Systems
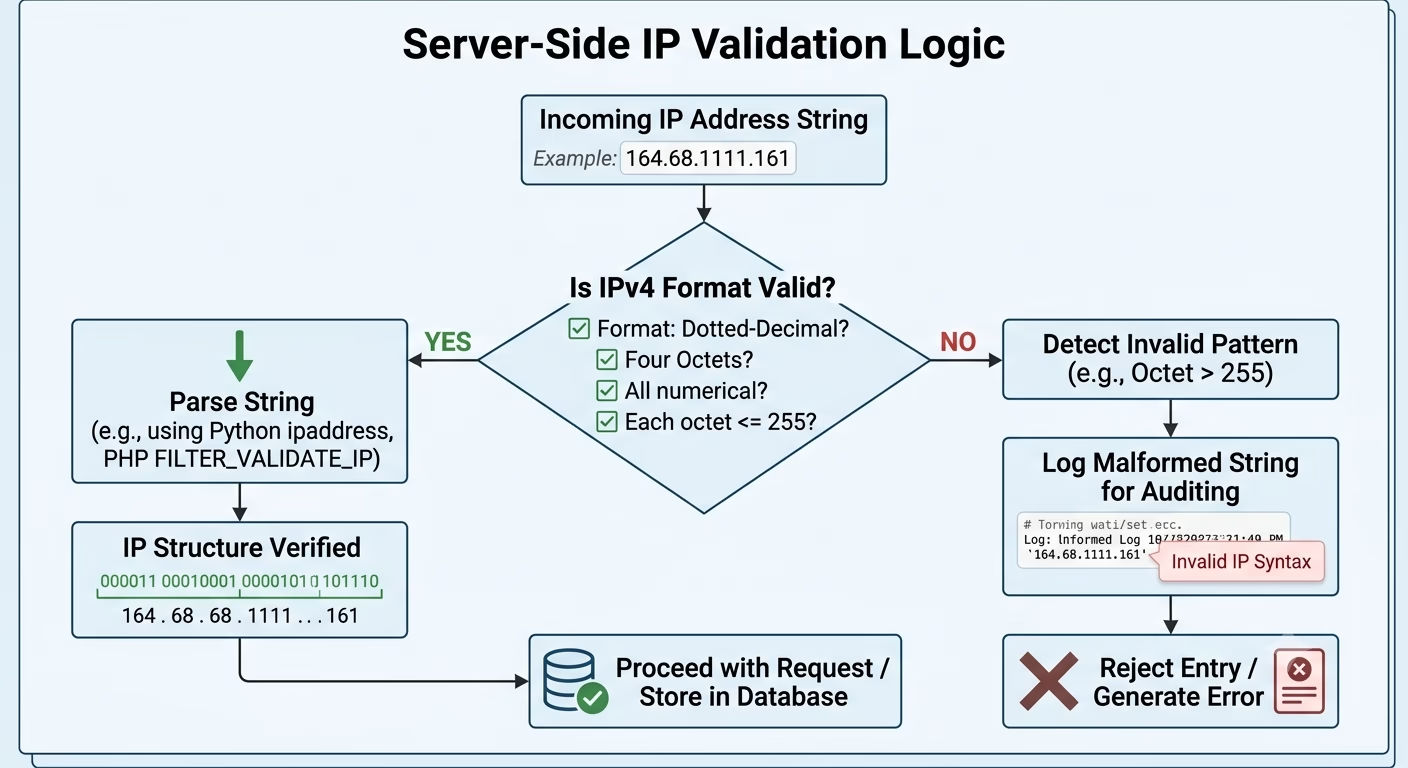
To prevent security flaws when accepting network inputs, follow the OWASP input validation guidelines for sanitizing user-submitted IP strings like 164.68.1111.161 from entering databases or causing backend crashes, implement robust validation at entry points.
Using Regular Expressions (Regex) for IP Validation
A common mistake developers make is using a simplistic regex pattern like \d{1,3}\.\d{1,3}\.\d{1,3}\.\d{1,3}. This pattern is flawed because it incorrectly marks invalid strings like 164.68.1111.161 or 999.999.999.999 as valid.
Strict IPv4 Validation Regex Pattern
Use a strict regex pattern that restricts each numerical group to the range 0–255:
^(?:(?:25[0-5]|2[0-4][0-9]|[01]?[0-9][0-9]?)\.){3}(?:25[0-5]|2[0-4][0-9]|[01]?[0-9][0-9]?)$
How this regex evaluates each octet:
25[0-5]: Matches numbers from 250 to 255.2[0-4][0-9]: Matches numbers from 200 to 249.[01]?[0-9][0-9]?: Matches numbers from 0 to 199 (including optional single and double digits).
Native Language Libraries (Recommended Over Regex)
While regex works well for client-side form validation, backend systems should rely on native socket or IP parsing libraries:
Python:
Pythonimport ipaddress try: ip = ipaddress.ip_address("164.68.1111.161") except ValueError: print("Invalid IPv4 address format.")PHP:
PHP$ip = "164.68.1111.161"; if (!filter_var($ip, FILTER_VALIDATE_IP, FILTER_FLAG_IPV4)) { echo "Invalid IPv4 address format."; }JavaScript (Node.js):
JavaScriptconst net = require('net'); console.log(net.isIPv4("164.68.1111.161")); // Returns false
How to Convert Valid IPv4 Addresses (Binary, Hexadecimal, Integer)
Once an IP address is corrected (for example, assuming the intended valid IP was 164.68.11.161), network systems often represent it in alternative numerical bases for routing tables, access control lists (ACLs), or database storage.
Here is how to convert the valid address 164.68.11.161 into binary, hexadecimal, and decimal integer formats.
1. Converting IPv4 to Binary
To convert 164.68.11.161 to binary, convert each decimal octet into its 8-bit equivalent:
164$= 128 + 32 + 4 = \mathbf{10100100}_2$68$= 64 + 4 = \mathbf{01000100}_2$11$= 8 + 2 + 1 = \mathbf{00001011}_2$161$= 128 + 32 + 1 = \mathbf{10100001}_2$
Binary Representation: 10100100.01000100.00001011.10100001
2. Converting IPv4 to Hexadecimal
Hexadecimal notation (base-16) is frequently used in network packet captures and low-level socket diagnostics. Convert each octet to two hex digits:
164$= \mathbf{\text{A4}}_{16}$68$= \mathbf{44}_{16}$11$= \mathbf{0B}_{16}$161$= \mathbf{\text{A1}}_{16}$
Hexadecimal Representation: A4.44.0B.A1 (or 0xA4440BA1)
3. Converting IPv4 to 32-Bit Decimal Integer
Databases often store IPv4 addresses as unsigned 32-bit integers to save space and speed up indexing.
Using 164.68.11.161:
$164 \times 16,777,216 = 2,751,463,424$
$68 \times 65,536 = 4,456,448$
$11 \times 256 = 2,816$
$161 \times 1 = 161$
Sum: $2,751,463,424 + 4,456,448 + 2,816 + 161 = \mathbf{2,755,922,849}$
Quick Reference: IPv4 Format Conversions
| Format | Notation / Value for 164.68.11.161 | Primary Use Case |
| Dotted Decimal | 164.68.11.161 | Human readability, UI configs |
| Binary | 10100100.01000100.00001011.10100001 | Subnetting, bitmasking, router hardware |
| Hexadecimal | 0xA4440BA1 | Wireshark captures, memory dumps |
| 32-bit Integer | 2755922849 | Database storage, IP indexing |
Real-World Impacts of Malformed IP Strings in Network Logs
Leaving invalid IP strings like 164.68.1111.161 unhandled in your software pipeline can lead to operational issues:
Application Crashes: Uncaught exceptions when passing string inputs directly to IP parsing functions (such as
inet_atonin C or Python’sipaddressmodule) can cause background workers or API gateways to throw500 Internal Server Errorresponses.Security Bypass: Flawed validation logic that strips out invalid characters instead of rejecting the input outright can result in IP spoofing or allow malicious traffic past IP-based access control lists (ACLs).
Failed WHOIS Telemetry: Security Information and Event Management (SIEM) tools like Splunk or Elastic Security fail to enrich log data when encountering malformed strings, resulting in missing threat intelligence and broken geo-IP lookups.
Frequently Asked Questions (FAQ)
What makes 164.68.1111.161 an invalid IP address?
An IPv4 address consists of four 8-bit numbers (octets) separated by dots. The maximum value for any 8-bit number in base-10 is 255. The segment 1111 exceeds this maximum limit, making the address invalid under RFC 791 protocol rules.
How can I find the correct IP if I see 164.68.1111.161 in server logs?
Check adjacent log entries or review your string parsing script. The string is almost certainly a typographical error for a valid IP address such as 164.68.11.161 or 164.68.111.161, caused by a duplicated key press or improper log concatenation.
Is 164.68.1111.161 an IPv6 address?
No. IPv6 addresses are 128-bit numbers divided into eight groups of four hexadecimal digits separated by colons (for example, 2001:0db8:85a3:0000:0000:8a2e:0370:7334). The string 164.68.1111.161 follows dotted-decimal IPv4 formatting, but contains invalid values.
Can I convert an invalid IP address like 164.68.1111.161 to binary or hex?
No. Conversion algorithms require each octet to be a valid 8-bit integer (0–255). Because 1111 cannot fit into an 8-bit binary structure ($1111_{10}$ requires 11 bits), conversion tools will throw an error until the typo is corrected.
How do I prevent users from submitting invalid IP addresses in web forms?
Use strict input validation on both the client side and server side. On the client side, use HTML5 pattern matching or strict regular expressions. On the server side, validate the string using built-in network socket functions like Python’s ipaddress or PHP’s filter_var().
About the Author
Steve Smith is a cybersecurity researcher and technical writer specializing in network diagnostics, WHOIS intelligence, and threat telemetry. With a background in systems analysis, Steve translates complex IP routing data, server logs, and security infrastructure into actionable insights for webmasters and network administrators. When not analyzing network traffic, he focuses on making web security accessible to everyday internet users.